Cybersecurity
After PHP2Shell: How AI Changes the Assessment of Cybersecurity MeasuresThe PHP2Shell disclosures put vulnerability response, AI-agent access and incident reporting under scrutiny. What NIS2, the Cyber Resilience Act and GDPR require—and which decisions organisations should document now.
The PHP2Shell disclosures put vulnerability response, AI-agent access and incident reporting under scrutiny. What NIS2, the Cyber Resilience Act and GDPR require—and which decisions organisations should document now.
Complex law. Clear action.
Reviewed by Oleksandr Sobovyi, Founder & CEO of CORVUS AI — editorial responsibility statement below.
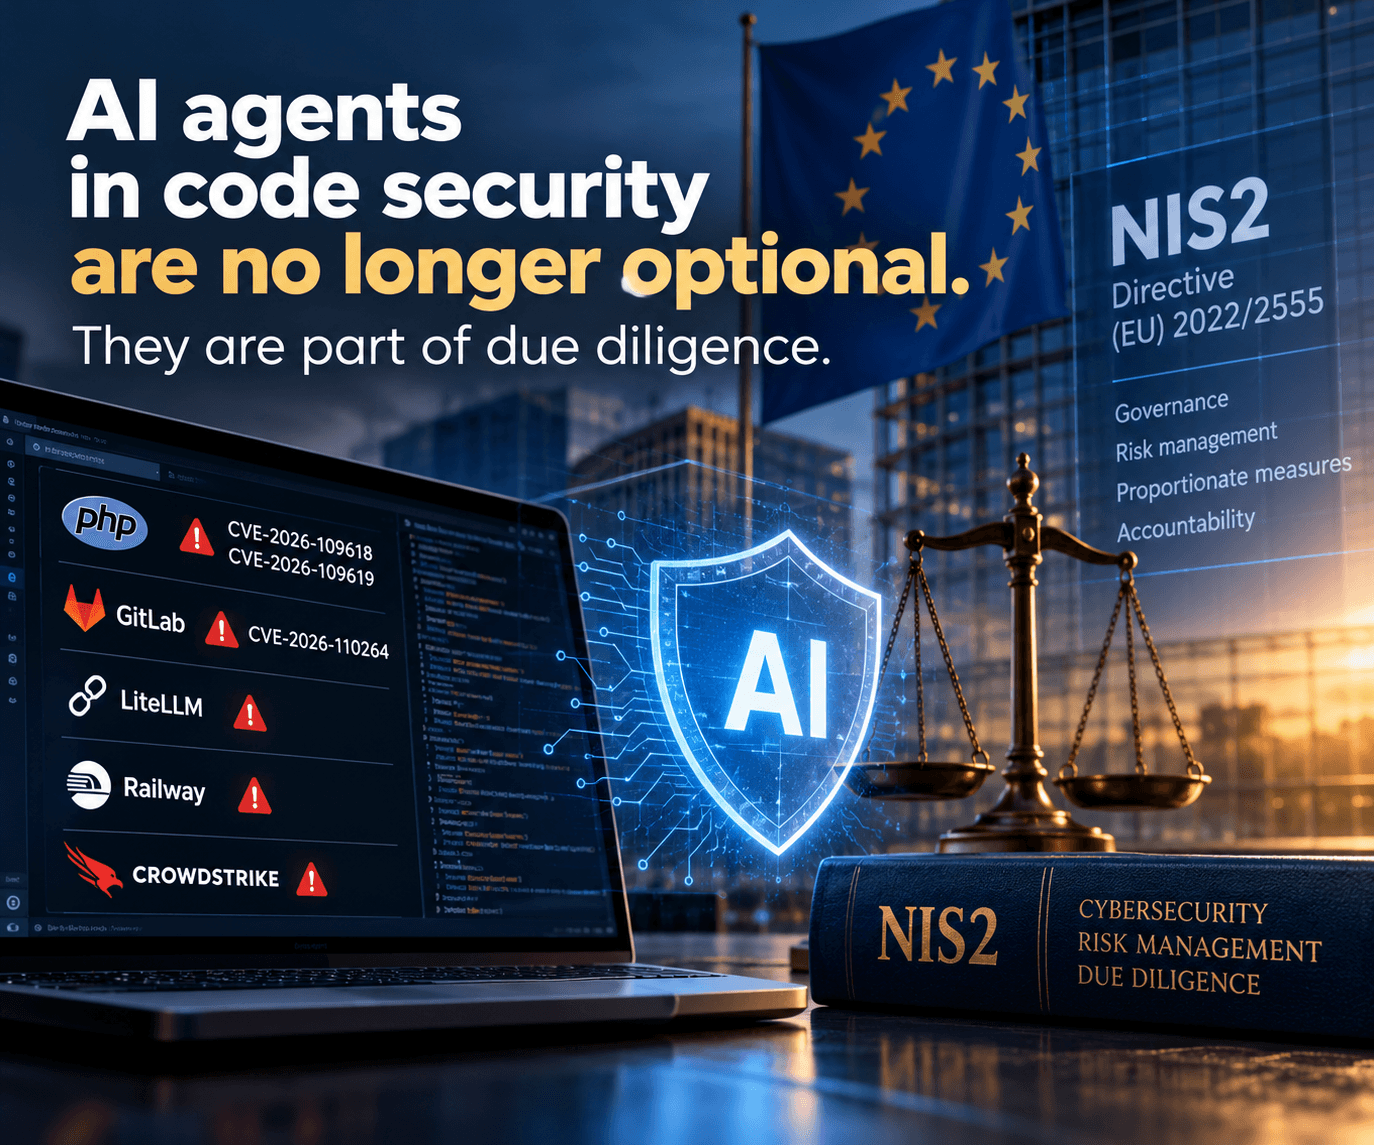
The disclosures published on 21 October by PHP, GitLab, LiteLLM, Railway and CrowdStrike expose a common governance problem: organisations must reassess both the speed of attacks and the authority they give to AI tools. EU law requires proportionate protection. Whether agents belong in that protection depends on evidence, effectiveness and the risks of deployment.
Five disclosures, one management problem
PHP released versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35 to address CVE-2026-109618 and CVE-2026-109619. Under particular conditions, the flaws allow unauthenticated remote code execution. Apache deployments using mod_php are a priority, although other configurations are also affected.
According to the PHP Foundation, a PHP developer found the first signs of the out-of-memory problem in 2024 while addressing an issue identified during a Quarkslab audit. Potential exploitation was considered, but concrete attack paths had not been established. Compatibility concerns, limited resources and difficulties choosing a fix also delayed remediation. Later research clarified the impact. Wiz reports using AI tools to develop and validate exploits against vulnerabilities in longstanding code.
This history supports a specific conclusion: an earlier assessment of practical exploitability may become unreliable as research capabilities improve. It does not establish that every vulnerability previously accepted as low risk is now exploitable.
GitLab's critical release addressed CVE-2026-110264, rated CVSS 10.0, involving integer overflow in regular-expression compilation. GitLab urged affected self-managed installations to update immediately.
LiteLLM reported a compromised release pipeline that distributed malicious version 1.107.0 through PyPI and container registries. Its preliminary account describes GitHub CLI OAuth tokens appearing in logged model responses and their suspected use to compromise release controls. The official source tag did not contain the malicious files; the published artifacts came from an attacker-controlled repository. Parts of the attack chain remain under investigation.
Railway disclosed possible access to customer environment variables, including decrypted contents in some cases, and recommended precautionary credential rotation. Separately, CrowdStrike reported campaigns in which attackers used agents to select tasks and execute commands. Its findings included a dual-agent framework targeting healthcare organisations in Argentina.
These are different events. Together, they justify reviewing vulnerability response, privileged access and supplier incident procedures.
NIS2: reassess the protection, then choose the tools
Under Articles 20 and 21 of Directive (EU) 2022/2555, management bodies approve cybersecurity risk-management measures and oversee implementation. The assessment considers the state of the art alongside implementation costs, organisational size, exposure and incident likelihood and severity. Vulnerability handling, supply-chain security and access controls are expressly covered. In the Netherlands, the Cyberbeveiligingswet has applied since 15 August 2026.
CORVUS AI's assessment is that AI-assisted exploitation strengthens the case for reviewing assumptions about response time and exploitability. It does not create a general duty to deploy agents. Effective conventional automation, managed services or well-resourced manual processes may also be appropriate. An agent with excessive privileges can introduce additional exposure.
Management should require evidence that the chosen process works: asset coverage, timely assessment, effective remediation and documented exceptions. Material risk decisions should follow the organisation's escalation framework. Article 20 does not prescribe a board resolution for every vulnerability reassessment.
CRA: identify the manufacturer and the reporting trigger
Article 14 of the Cyber Resilience Act has applied since 11 September 2026. Manufacturers must report actively exploited vulnerabilities affecting covered products to the coordinating CSIRT and ENISA through the single platform: without undue delay, with 24-hour early warning, 72-hour notification and a final report within 14 days after a corrective or mitigating measure becomes available.
Public proof-of-concept code alone does not establish active exploitation. Amazon has reported attempts from 17 October, while noting uncertainty about their success against real systems. These facts require assessment against Article 3(42); the clock cannot be postponed by an internal decision.
Using PHP or GitLab does not itself establish manufacturer status. Product supply and role matter; standalone SaaS generally falls outside scope, subject to the remote-data-processing boundary. Article 24's steward regime generally applies from December 2027. Article 64's general fines regime also applies from 11 December 2027: up to the higher of €15 million or 2.5% of worldwide annual turnover for relevant infringements, subject to statutory exceptions.
The joint statement published by ENISA and other EU authorities confirms the reporting date and immediate remediation priorities.
Agent access and model logs need explicit controls
The LiteLLM incident disclosure illustrates how model-response logging can turn an operational feature into a route to privileged credentials. Its preliminary findings should remain attributed to the company rather than presented as a completed forensic conclusion.
An agent is a technical identity with permissions. It needs access boundaries, accountable ownership and revocation procedures. NIS2 access-control requirements are relevant for entities within scope; GDPR Article 32 applies where personal data are processed.
Logs can contain credentials, personal data and confidential material. Retention limits, access restrictions and appropriate security measures should reflect their contents and purpose. Secrets should be filtered before storage wherever feasible, with existing logs checked for exposure. These are risk-management recommendations, not a universal statutory prescription for one architecture.
Article 4 of the AI Act, as amended in July 2026, requires providers and deployers to take measures supporting staff AI literacy. It does not guarantee an individual competence level. For teams using coding agents, training should address credential exposure, permissions, unsafe commands and review of proposed changes.
Railway: rotation and notification are separate decisions
Credential rotation contains exposure; it does not determine whether a personal data breach occurred. Credentials are not always personal data themselves, but may relate to an identifiable person or enable access to personal information.
Under GDPR Article 33, controllers notify the competent supervisory authority without undue delay and, where feasible, within 72 hours of awareness, unless the breach is unlikely to create a risk to individuals' rights and freedoms. Processors notify controllers without undue delay. All personal data breaches must be documented, including those not notified. Article 34 separately addresses communication to individuals where high risk is likely, subject to its exceptions.
Customers should establish which systems the exposed secrets could access, assess evidence of misuse and record the reasoning. A completed forensic investigation is not a prerequisite to every notification; information can be supplied in stages.
Health data fall within Article 9's special categories. Financial and security-related information may be highly sensitive without automatically belonging to those categories. That distinction matters when assessing consequences and safeguards.
What organisations should do now
Identify and contain exposure immediately. Prioritise internet-facing PHP and affected self-managed GitLab. Patch or isolate exposed systems where prompt remediation is unavailable. Continue the wider asset inventory in parallel.
Investigate compromised artifacts and secrets. Check LiteLLM package versions and container digests against the incident disclosure. A later execution of an affected downloaded image can still matter. Rotate exposed credentials, preserve evidence and investigate affected environments.
Assess reporting duties separately. Establish the relevant entity, product, incident and awareness timeline. Review CRA, GDPR and, for entities within scope, NIS2 Article 23 significant-incident reporting. Avoid treating a public advisory as either automatic proof of a reportable breach or a reason to wait.
Restrict agent permissions. Prefer separate identities and short-lived, narrowly scoped credentials. Keep organisation-owner tokens out of agent-accessible environments. Require review and testing before material production changes.
Reassess accepted risks. Focus on decisions materially dependent on low practical exploitability or long expected attack-development times. Record the evidence, compensating controls, responsible owner and escalation decision.
Review supplier contracts. Check incident-notification timing, cooperation, access to evidence, audit arrangements and liability allocation. Ensure internal response procedures can operate within applicable reporting deadlines.
The immediate legal task is to establish exposure, regulated roles and reporting triggers. The management task is to demonstrate that protection remains effective as attack capabilities change. Agent adoption should follow that assessment, with controls proportionate to the authority the agent receives.
Oleksandr Sobovyi
Founder & CEO, CORVUS AI
Netherlands | contact@corvusai.eu
Disclaimer
This article has been prepared by CORVUS AI for general informational and educational purposes only. It is intended to make complex legal and regulatory developments easier to understand.
It does not constitute legal advice and does not create a professional adviser–client relationship. The information should not be relied upon as a substitute for advice based on the specific facts, circumstances and applicable law relevant to your organisation or project.
The article reflects our understanding of the law and regulatory framework as of the date of publication. Legislation, case law, regulatory guidance and administrative practice may subsequently change. While reasonable care has been taken in preparing this article, CORVUS AI does not warrant that the information is complete or remains current after the date of publication. We do not undertake to update this content.
To the fullest extent permitted by applicable law, CORVUS AI excludes liability for loss arising from reliance on this article. Nothing in this article constitutes an offer or solicitation to provide regulated legal services in any jurisdiction where doing so would be unlawful.
AI-assisted preparation: This article was prepared with the assistance of AI tools. Its legal analysis, conclusions and final text were subject to human review and editorial control and were reviewed and approved prior to publication by Oleksandr Sobovyi, Founder & CEO of CORVUS AI. CORVUS AI retains editorial responsibility for the published content.
For advice tailored to your organisation, project or specific circumstances, please contact CORVUS AI.
This analysis reflects information available on 22 October 2026. The LiteLLM and Railway investigations remain ongoing; company and threat-intelligence findings are attributed to their respective issuers. It provides general legal information rather than advice on a specific incident.
Editorial transparency: prepared with assistance from AI tools. Editorial responsibility: Oleksandr Sobovyi, Founder & CEO, CORVUS AI.
Legal references — European Union
Cyber Resilience Act, Articles 3, 14, 24, 64 and 71
GDPR, Articles 4, 9 and 32–34.
AI Act, consolidated version of 27 July 2026, Articles 4 and 50.
